23. oktober 2026
php2shell scanner
github.com
A high-fidelity scanner for the PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619.
23. oktober 2026
Node.js security releases - 21 October 2026
nodejs.org
Node.js security updates for the 26.x, 24.x and 22.x release lines, covering high and medium severity vulnerabilities and dependency updates.
23. oktober 2026
MCP Game Hacking
github.com
An MCP server and structured knowledge base for game hacking and reverse engineering, with specialized agents and workflow tools.
23. oktober 2026
Cloudflare Security Audit Skill
github.com
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings.
11. oktober 2026
trailofbits/skills
github.com
Agent skills from Trail of Bits for security analysis, vulnerability research and audit workflows.
6. oktober 2026
morluto/rea
github.com
An MCP tool for investigating application behaviour, binaries and runtime activity with coding agents.
30. september 2026
aquasecurity/trivy
github.com
A security scanner for vulnerabilities, exposed secrets and configuration problems across containers, infrastructure and repositories.
30. september 2026
bridgecrewio/checkov
github.com
Checks infrastructure definitions, container images and dependencies for security weaknesses before deployment.
30. september 2026
ossf/scorecard
github.com
Automated checks that help assess the security practices of open-source projects.
17. september 2026
Kobra / React Input OTP component
kobra.systems
A React component for entering one-time verification codes, with segmented fields and styled interaction states.
4. september 2026
Cloud FAQ - Codex Security | ChatGPT Learn
learn.chatgpt.com
Documentation about Codex Security Cloud repository scans, findings and remediation workflows.
4. september 2026
Secret scanning coverage updates - GitHub Changelog
github.blog
GitHub describes additions to secret detection, push protection and security alert metadata.
4. september 2026
CLI quickstart - Codex Security | ChatGPT Learn
learn.chatgpt.com
Instructions for running local Codex Security scans and reviewing vulnerability reports and coverage.
4. september 2026
‘Vibecoding’ Privacy Risks Require Keeping Humans in the Loop
news.bloomberglaw.com
An article examining privacy risks in AI-generated applications and the role of human security review.
4. september 2026
August 2026 Security Release
nextjs.org
Release notes for Next.js security updates, including affected versions and upgrade guidance.
4. september 2026
Securing your API | Supabase Docs
supabase.com
A guide to securing Supabase's Data API with database grants, row-level security and request checks.
4. september 2026
Catch security issues as Claude writes code - Claude Code Docs
code.claude.com
Documentation for a Claude Code plugin that reviews generated changes for common security vulnerabilities during development.
4. september 2026
openai.com/index/hugging-face-incident-and-the-road-ahead/
openai.com
4. september 2026
Scan your codebase for vulnerabilities - Claude Code Docs
code.claude.com
Instructions for using Claude Security to scan a codebase, review vulnerability findings and prepare fixes.
4. september 2026
Critical remote code execution in Serena, a popular MCP coding agent
about.gitlab.com
GitLab's analysis of a remote-code-execution vulnerability in the Serena coding agent and its remediation.
26. juni 2026
privacypolicies.com/
privacypolicies.com
19. juni 2026
dani-garcia/vaultwarden
github.com
An independently developed Rust server compatible with Bitwarden password-manager clients.
12. juni 2023
shaurya-007/NSA-Linux-Hardening-docs
github.com
A repository collecting documents about strengthening Linux system security.
18. april 2023
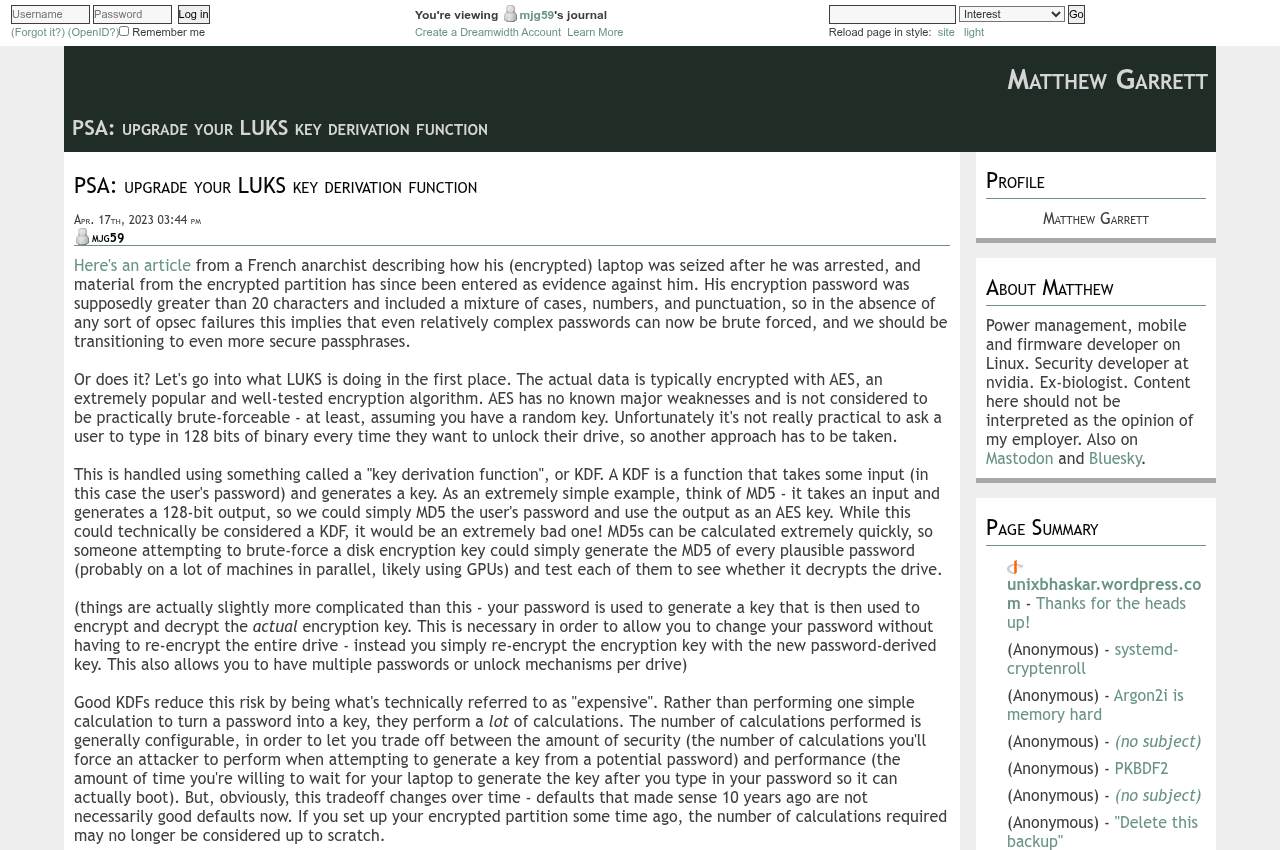
PSA: upgrade your LUKS key derivation function
mjg59.dreamwidth.org
Here's an article from a French anarchist describing how his (encrypted) laptop was seized after he was arrested, and material from the encrypted partit.
15. februar 2023
Infosec Exchange
infosec.exchange
A Mastodon instance for info/cyber security-minded people
24. januar 2023
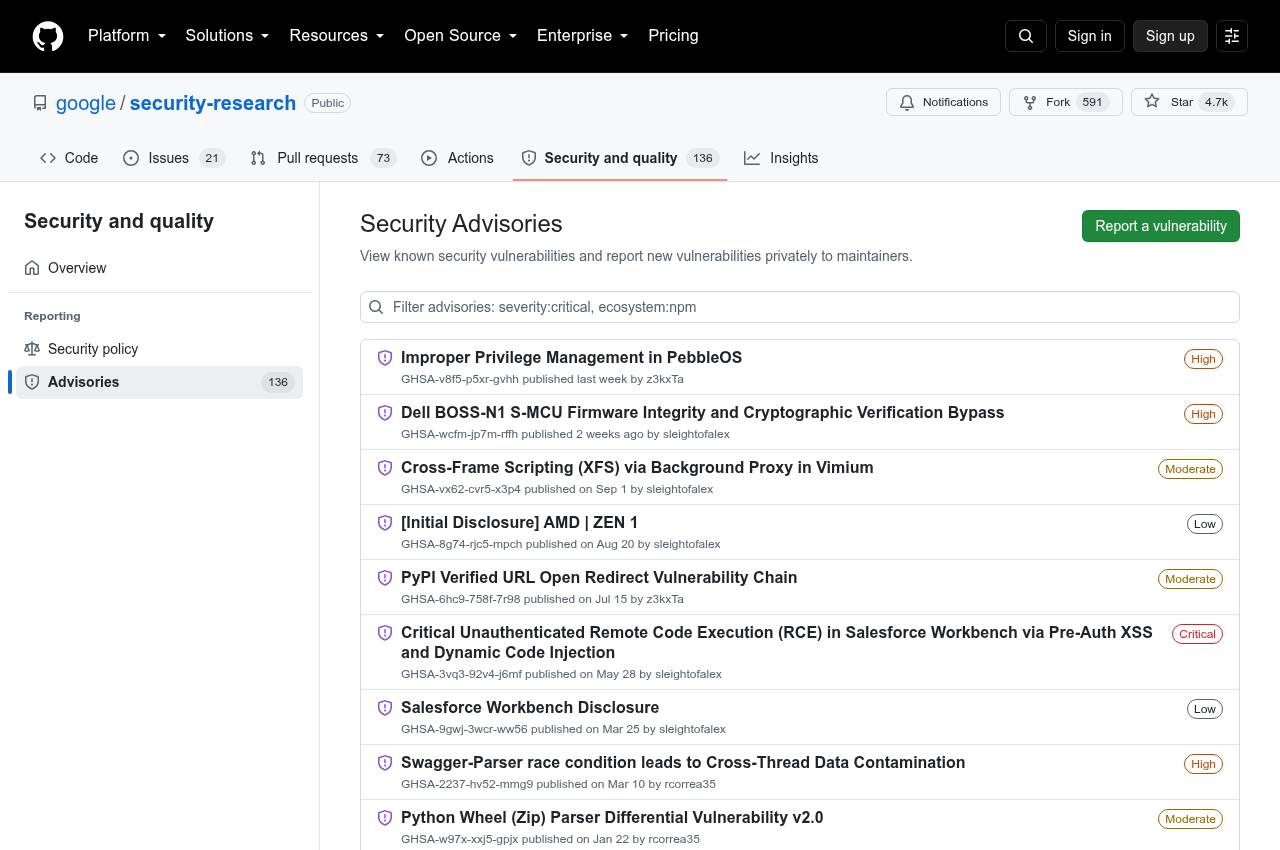
Build software better, together
github.com
Google’s security-research advisory listing on GitHub. The fetched page exposed only generic site metadata.
3. februar 2022
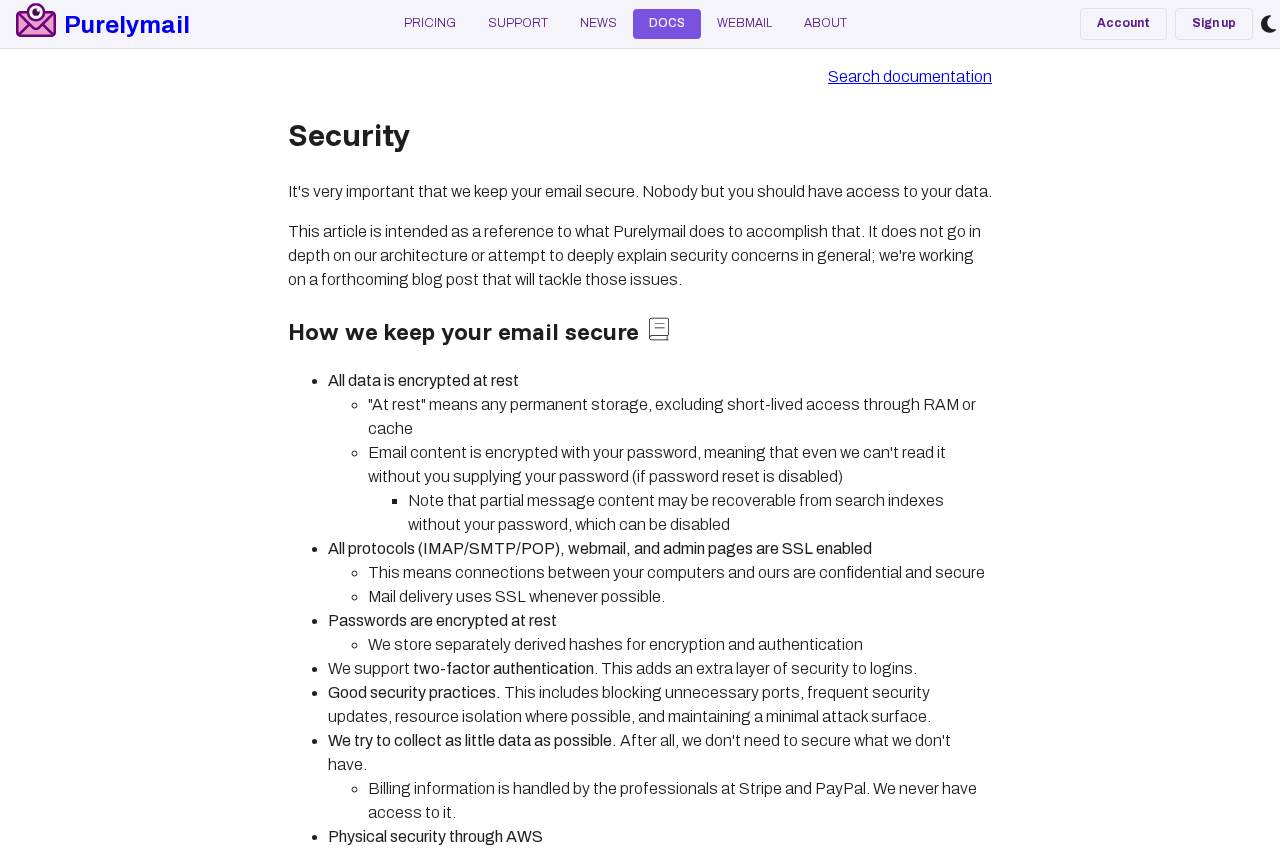
Security | Purelymail
purelymail.com
Purelymail’s documentation explaining security practices for its email service.
31. januar 2022
Let's Encrypt wildcard certificate with acme.sh and Cloudflare DNS
cyberciti.biz
24. november 2021
New JavaScript malware works as a "RAT dispenser"
therecord.media
Cybersecurity experts from HP said they discovered a new strain of JavaScript malware that criminals are using as a way to infect systems and then deploy much dangerous remote access trojans (RATs)
31. oktober 2021
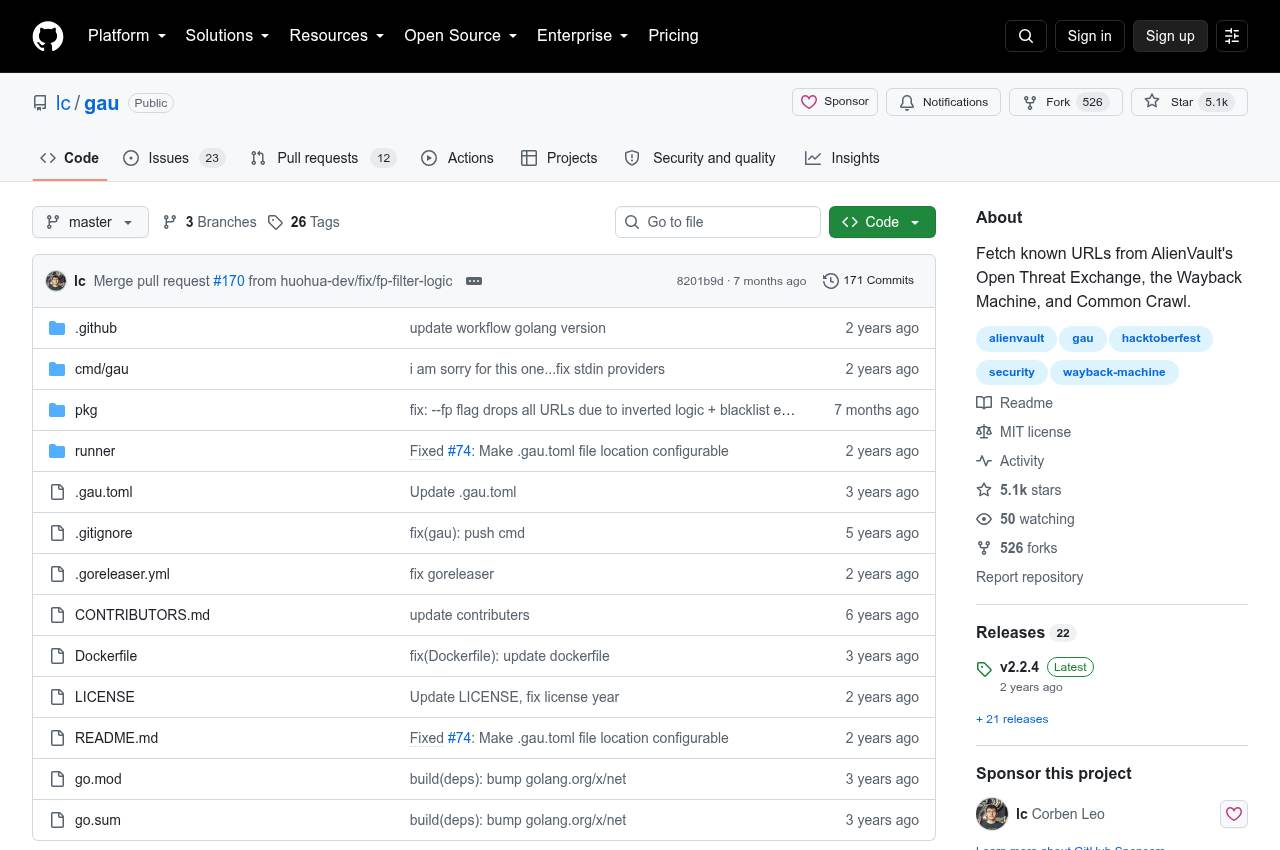
lc/gau
github.com
A reconnaissance utility that gathers previously indexed URLs from public archival and threat-intelligence sources.
21. september 2021
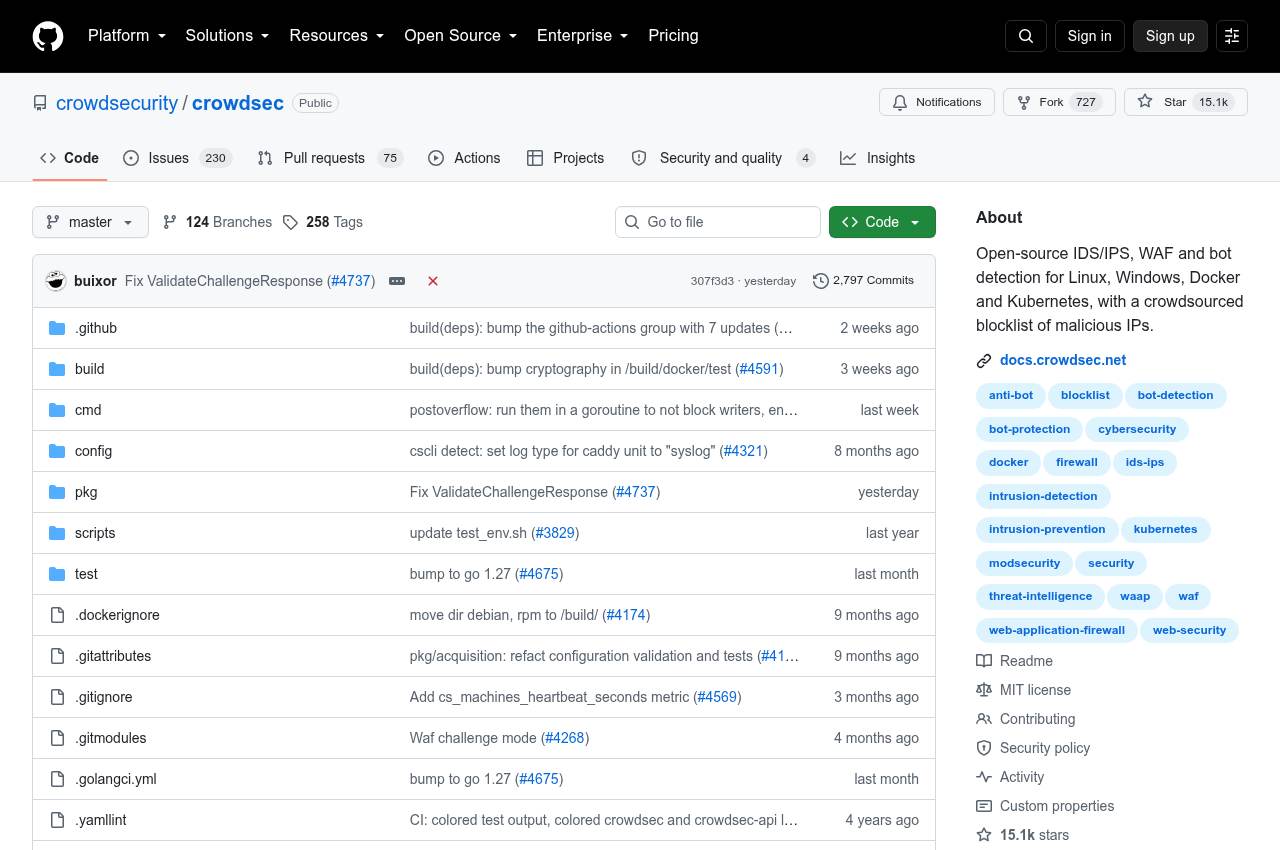
crowdsecurity/crowdsec
github.com
Security software combining intrusion detection, web protection and a shared malicious-IP blocklist.
20. marts 2021
stackrox/Kubernetes_Security_Specialist_Study_Guide
github.com
Study material for the Certified Kubernetes Security Specialist examination.
8. februar 2021
tsoungui.fr/ebooks/Hardening%20Linux.pdf
tsoungui.fr
A downloadable book about strengthening the security of Linux systems. Full PDF contents were not summarised.
30. januar 2021
GrapheneOS: the private and secure mobile OS
grapheneos.org
A mobile operating system focused on privacy and security while retaining Android application compatibility.
28. december 2020
harsh-bothra/Bheem
github.com
A security-assessment framework that coordinates reconnaissance tools and organises their results.
13. december 2020
GitHub - mafintosh/hyperphone: A telephone over Hyperbeam
github.com
A telephone over Hyperbeam
4. november 2020
WPScan CLI Scanner Install + User Guide
wpscan.com
Installation and usage documentation for WPScan’s command-line WordPress security scanner.
29. september 2020
Let's Encrypt TLS with HAProxy Kubernetes Ingress
www.youtube.com
A video showing how to configure Let's Encrypt TLS certificates for the HAProxy Kubernetes Ingress Controller.
4. august 2020
medium.com/@OliverPifferi/nextcloud-releases-forms-to-protect-privacy-sensitive-survey-data-c780b5e1d4cd
medium.com
8. juli 2020
Git All The Payloads! A Collection Of Web Attack Payloads - PentestTools
pentesttools.net
A reference collection of web-security testing payloads.
1. juli 2020
Emil Stahl
emilstahl.dk
The personal website of cybersecurity specialist Emil Stahl.
15. februar 2020
GreyNoise | Real-Time Network Threat Intelligence
www.greynoise.io
A threat-intelligence service for interpreting network scanning activity and identifying active exploitation.
15. februar 2020
Shodan
www.shodan.io
A search service for discovering internet-connected devices and the services they expose.
12. februar 2020
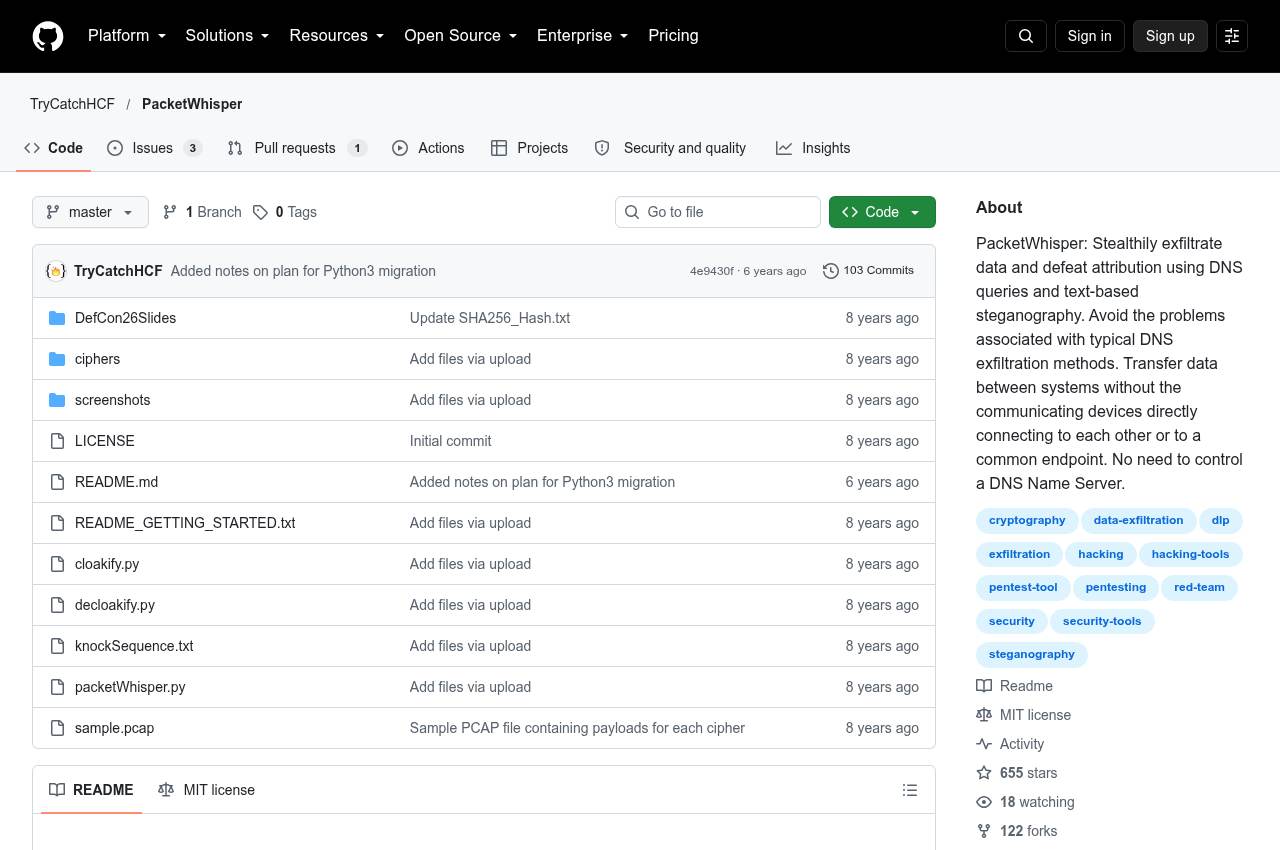
TryCatchHCF/PacketWhisper
github.com
A security-research tool exploring covert data transfer through DNS queries and text encoding.
28. januar 2020
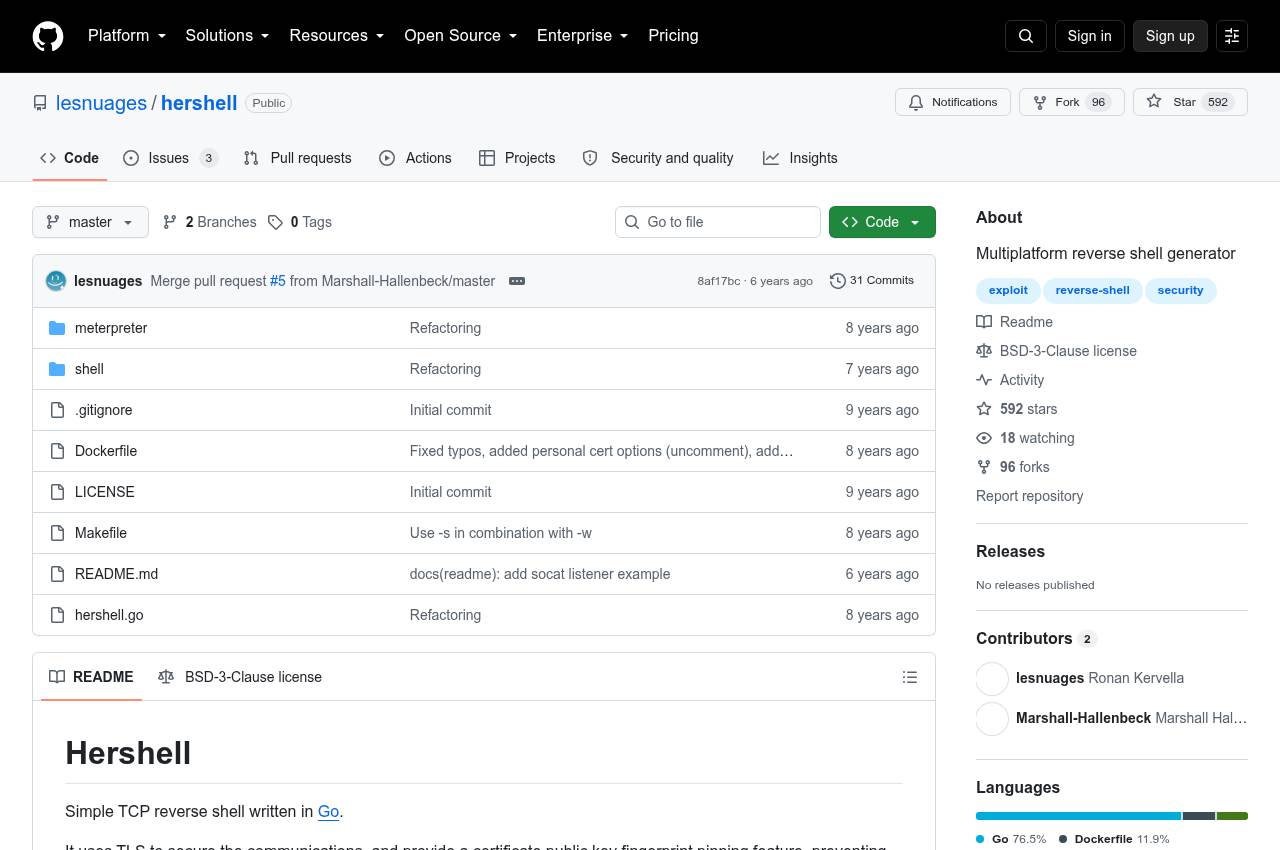
lesnuages/hershell
github.com
A cross-platform reverse-shell generator intended for security testing.
14. januar 2020
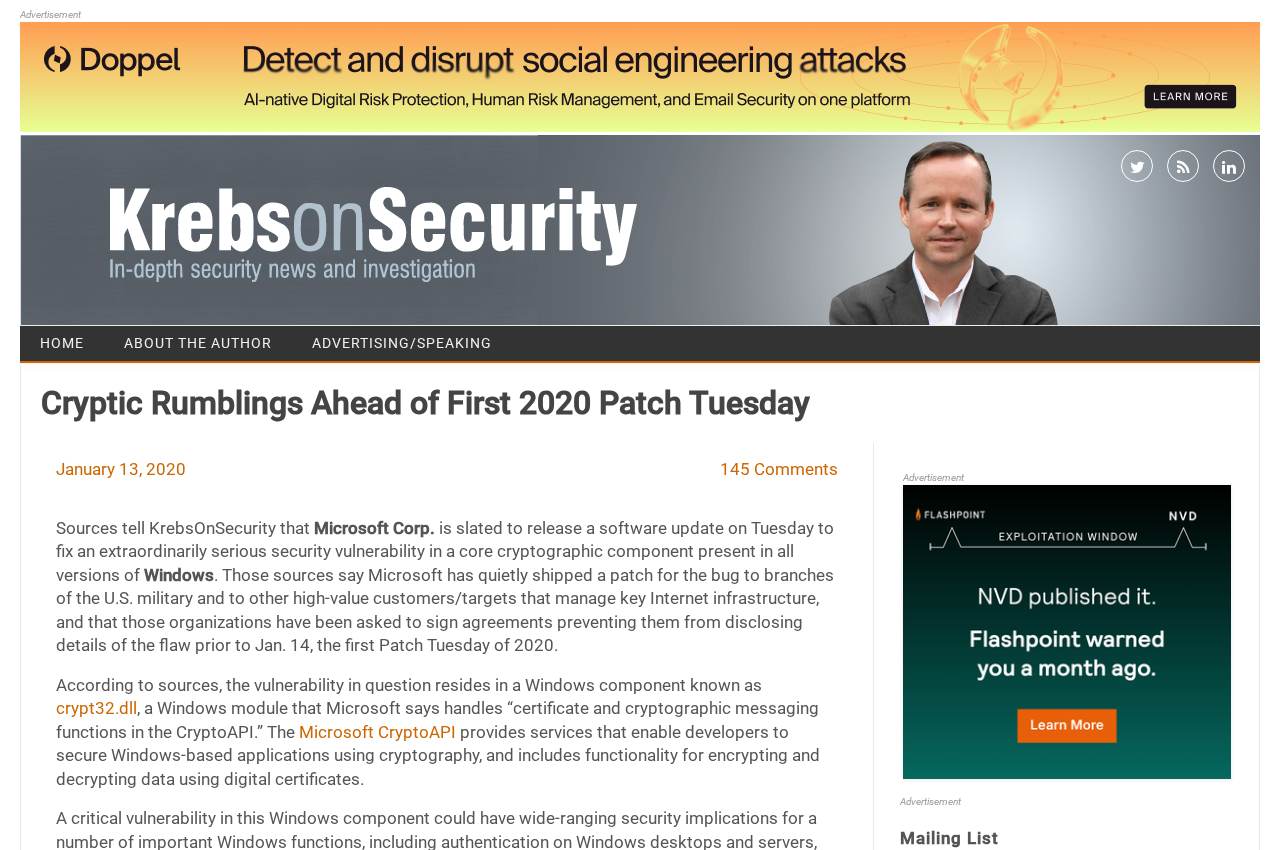
Cryptic Rumblings Ahead of First 2020 Patch Tuesday - Krebs on Security
krebsonsecurity.com
Historical reporting on security concerns preceding Microsoft’s first monthly patch release of 2020.
13. januar 2020
Pickfordmatt/SharpLocker
github.com
A security-testing demonstration of a counterfeit Windows lock screen, illustrating the risk of credential phishing.
20. november 2019
JWT Tool documentation
github.com
Documentation for a toolkit that inspects and tests JSON Web Tokens.
14. november 2019
AlisamTechnology/ATSCAN
github.com
A security-testing utility for search-based discovery and automated vulnerability scanning.
12. november 2019
s0md3v/Arjun
github.com
A security-testing utility for discovering HTTP request parameters.
9. november 2019
Image-to-Image Translation with Conditional Adversarial Networks
arxiv.org
The pix2pix paper investigates learning mappings between images, with applications including colourisation and generating pictures from edge or label maps. Summary based on its abstract.
30. oktober 2019
A Cybersecurity Firm’s Sharp Rise and Stunning Collapse
www.newyorker.com
Raffi Khatchadourian on Tiversa, which dominated an emerging online market before it was accused of fraud, extortion, and manipulating the federal government
30. oktober 2019
belane/CloudHunter
github.com
A security-auditing tool for discovering storage buckets across major cloud providers.
28. juni 2019
raw.githubusercontent.com/rebootuser/LinEnum/master/LinEnum.sh
raw.githubusercontent.com
The downloadable LinEnum shell script for enumerating Linux system configuration during security assessments.
20. juni 2019
OJ/gobuster
github.com
A Go utility for discovering web paths, virtual hosts and DNS names during authorised testing.
26. december 2018
malwoverview : Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia, Malware Bazaar, Thr
kitploit.com
An overview of a threat-investigation tool that queries multiple public malware and intelligence services.
22. december 2018
rada.re/r/
rada.re
The Radare project’s entry page for its reverse-engineering tools and releases.
22. december 2018
Apktool | Apktool
ibotpeaches.github.io
A utility for decoding and inspecting Android application packages during reverse engineering.
17. december 2018
SEKTOR7 Research Blog
blog.sektor7.net
A SEKTOR7 research article about in-memory techniques on Linux, within its security-research blog.
11. december 2018
emotet_research/doc/EN_emotet_packer_analysis_and_config_extraction_v1.pdf at master · d00rt/emotet_research
github.com
A downloadable security-research report on Emotet packing and configuration extraction. The PDF was not fully analysed.
11. december 2017
Encryption New on Minds | Minds
www.minds.com
A historical Minds announcement introducing encrypted messaging.
6. december 2017
Initial Server Setup with Ubuntu 16.04 | DigitalOcean
www.digitalocean.com
A historical checklist for initial Ubuntu 16.04 server configuration and basic access security.
18. november 2017
mushorg/glutton
github.com
A low-interaction honeypot for observing unsolicited connections and suspicious network behaviour.
23. oktober 2017
The command-line, for cybersec
blog.erratasec.com
An article discussing command-line skills relevant to cybersecurity work.
3. oktober 2017
Kendt dansk sikkerhedsmand advarer mod salgs-gas: "Jeg er meget bekymret over, at virksomheder kommer til at tro, de er compliant med GDPR, fordi de har købt en dims hos et sikkerh
www.computerworld.dk
A Danish interview warning against treating security-product purchases as proof of GDPR compliance.
16. september 2017
DMARC dot DK
dmarc.dk
Danish information about DMARC email authentication and its role in reducing impersonation.
8. august 2017
TFHE Fast Fully Homomorphic Encryption over the Torus
tfhe.github.io
A fast open-source library for fully homomorphic encryption
10. juli 2017
Upgrading Simple Shells to Fully Interactive TTYs
blog.ropnop.com
A security-testing reference explaining the differences between basic remote shells and interactive terminals.
7. juli 2017
0x4D31/honeyLambda
github.com
A serverless monitoring project that creates decoy HTTP endpoints to detect suspicious access.
2. juni 2017
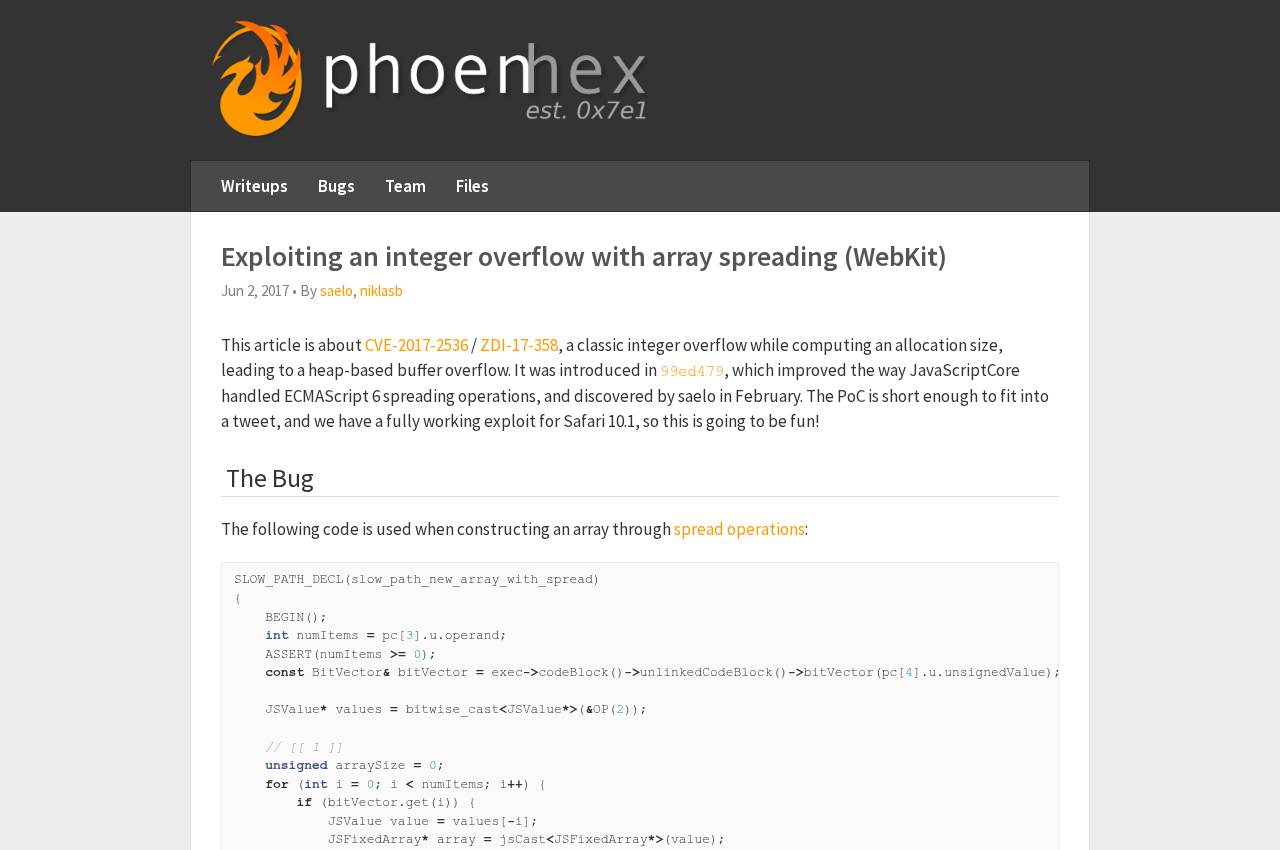
Exploiting an integer overflow with array spreading (WebKit) - phoenhex team
phoenhex.re
This article is about CVE-2017-2536 / ZDI-17-358 , a classic integer overflow while computing an allocation size, leading to a heap-based buffer overflow. It was introduced in 99ed479 , which improved the way JavaScriptCore handled.
14. maj 2017
Exploitation Chronomancy: Temporal Return Addresses
hick.org
ToorCon 2005 presentation slides on temporal return addresses and exploitation techniques.
8. maj 2017
When You Accidentally Break Your School Network in 1995
mmccaff.github.io
In my last post, I reminisced about my bbs software that I wrote and sold in 1993. In 1995, I was a senior in high school, and my school had just purchased a 76 computer Novell network for the 900
5. maj 2017
GitHub - Choudai/R10: Lightweight Ransomware @Choudai
github.com
Lightweight Ransomware @Choudai
19. april 2017
Create a temporary random filename in Bash
www.cyberciti.biz
10. april 2017
CAA checking becomes mandatory for SSL/TLS certificates
ma.ttias.be
A look at the CAA DNS record (Certificate Authority Authorization), what it does, and why Certificate Authorities are now required to check it before issuing an ….
15. februar 2017
Deception: turning the tables on your adversaries
medium.com
28. januar 2017
Hacker OPSEC
grugq.github.io
Think of Mujahideen Secrets as a branded promotional tool, sort of like if Manchester United released a branded fan chat app. Although there has been ….
14. december 2016
Grean easyID and Auth0
grean.com
13. august 2016
Dedup Est Machina
www.ieee-security.org
A 2016 security paper examining how memory deduplication can become a timing side channel and aid Rowhammer exploitation.
11. august 2013
express-brute
npmjs.org
Middleware that rate-limits Express routes to help protect against brute-force requests.